- Trending
- Comments
- Latest
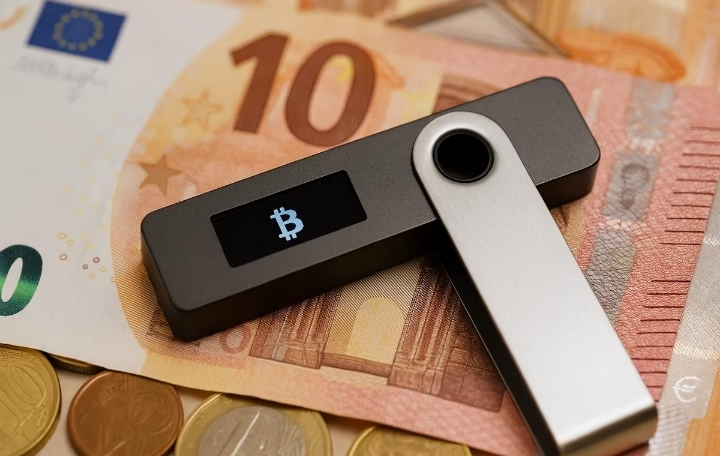
Crypto wallet manufacturers selling qualifying hardware and software products in the European Union now face a new 24-hour deadline to alert regulators when their products are hit by actively exploited vulnerabilities or severe security incidents.
The requirement took effect on September 11, 2026, under the EU’s Cyber Resilience Act, or CRA, for the start of a faster reporting system for cybersecurity incidents involving products with digital elements.
The rules can cover commercially supplied connected hardware wallets and downloadable wallet software when they meet the CRA’s requirements for products placed on the EU market. However, the rules do not automatically mean every wallet brand or crypto project is covered.
Under the new system, manufacturers must submit an early warning without undue delay and no later than 24 hours after becoming aware of an actively exploited vulnerability or severe security incident.
A fuller notification must then follow within 72 hours.
For actively exploited vulnerabilities, the final report is due no later than 14 days after a corrective or mitigating measure becomes available. For severe incidents, the final report is due within one month of the 72-hour notification.
The EU’s reporting timetable is designed to give regulators and cybersecurity teams information about serious vulnerabilities while there is still time to limit their impact.
The CRA is a broad EU product-security law covering hardware and software products with digital elements made available on the European market.
That means a commercially supplied connected hardware wallet or downloadable wallet application can potentially fall within its scope if it meets the legal requirements.
But the rules are not simply a blanket regulation covering every crypto wallet.
The European Commission says the specific product, how it is supplied and whether an exclusion applies all matter when determining whether a manufacturer has obligations under the law.
This definitely matters for the crypto industry because wallet products vary widely. A hardware device sold commercially in Europe may face different obligations from an open-source project or software that is not supplied as a commercial product.
The new reporting process is also designed to centralise how cybersecurity incidents reach European authorities.
Manufacturers are required to submit their notifications through the EU’s Single Reporting Platform, operated by the European Union Agency for Cybersecurity, ENISA.
The platform allows manufacturers to report once instead of separately notifying multiple national authorities. Once a notification is submitted, the relevant coordinating Computer Security Incident Response Team can distribute the information to other national teams where necessary.
This means the new system is not simply about imposing a deadline. It is also intended to make the reporting and response process more coordinated across the EU.
The Single Reporting Platform became operational on September 11, the same day the CRA’s mandatory reporting obligations for manufacturers took effect.
Crypto wallets hold the keys that allow users to control digital assets, making vulnerabilities in wallet products particularly sensitive.
A flaw that exposes private keys, compromises transaction signing or allows an attacker to manipulate a wallet could potentially lead to direct financial losses.
But the wider crypto industry has also learned that security problems do not always begin with the blockchain itself.
The crypto security risks surrounding wallets, exchanges, employees and users can become just as important when criminals are looking for ways to access digital assets.
The new EU rules therefore put greater pressure on manufacturers to identify serious problems quickly and make sure regulators receive information before vulnerabilities become larger incidents.
One important part of the new reporting regime is that it is not limited to products launched after the CRA’s broader security requirements take effect.
The reporting obligations apply to qualifying products already placed on the EU market.
The broader CRA product-security requirements are scheduled to apply from December 11, 2027, but the mandatory reporting regime for actively exploited vulnerabilities and severe incidents started earlier, on September 11, 2026.
This creates a transition period in which manufacturers must already respond to serious security incidents even though many of the law’s wider product-security obligations have not yet taken effect.
The CRA also addresses open-source software, but its reporting obligations for open-source software stewards begin later.
According to ENISA, those obligations under Article 24(3) will apply from December 11, 2027.
This is also important because open-source software can play a major role in crypto infrastructure, including wallet applications and other blockchain tools.
The law also does not create a blanket exemption simply because software is open source. Commercially supplied free and open-source products can still fall within the manufacturer’s obligations depending on the circumstances.
The new EU reporting deadline comes as crypto users continue to deal with increasingly sophisticated attacks against wallets and digital-asset infrastructure.
Recent incidents have shown that criminals can exploit technical vulnerabilities, compromised credentials and social engineering rather than relying on a single method of attack.
The Bit Gazette previously examined how deepfake multisig attacks can target the people and processes controlling crypto treasuries.
The new EU rules approach the problem from another direction which is forcing manufacturers to report serious product vulnerabilities quickly enough for regulators and cybersecurity teams to respond.
For wallet makers, the question is no longer only whether a vulnerability can be fixed. It is also how quickly they can recognise an actively exploited flaw, report it and communicate the risk before it spreads.
The 24-hour reporting deadline puts a new clock on that process, while the 72-hour notification and later final reports create a longer chain of accountability.

Copyright © 2025 - The Bit Gazette.