- Trending
- Comments
- Latest

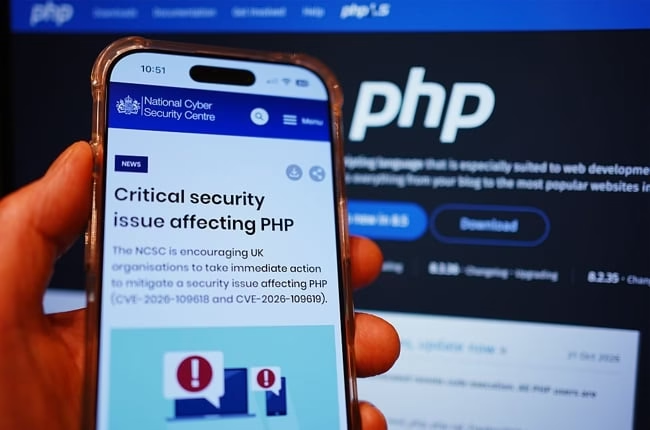
Attackers can take over servers running PHP without ever logging in, and they are already trying at scale. Cloudflare has seen millions of exploit attempts since two flaws, dubbed PHP2Shell, were disclosed on October 21, forcing governments, banks and airlines in Europe and Asia to suspend some online services.
On Thursday, October 22, Reuters reported that Cloudflare had observed millions of attempted exploits following the disclosure, as governments, businesses and technology providers raced to secure systems running affected versions of PHP.
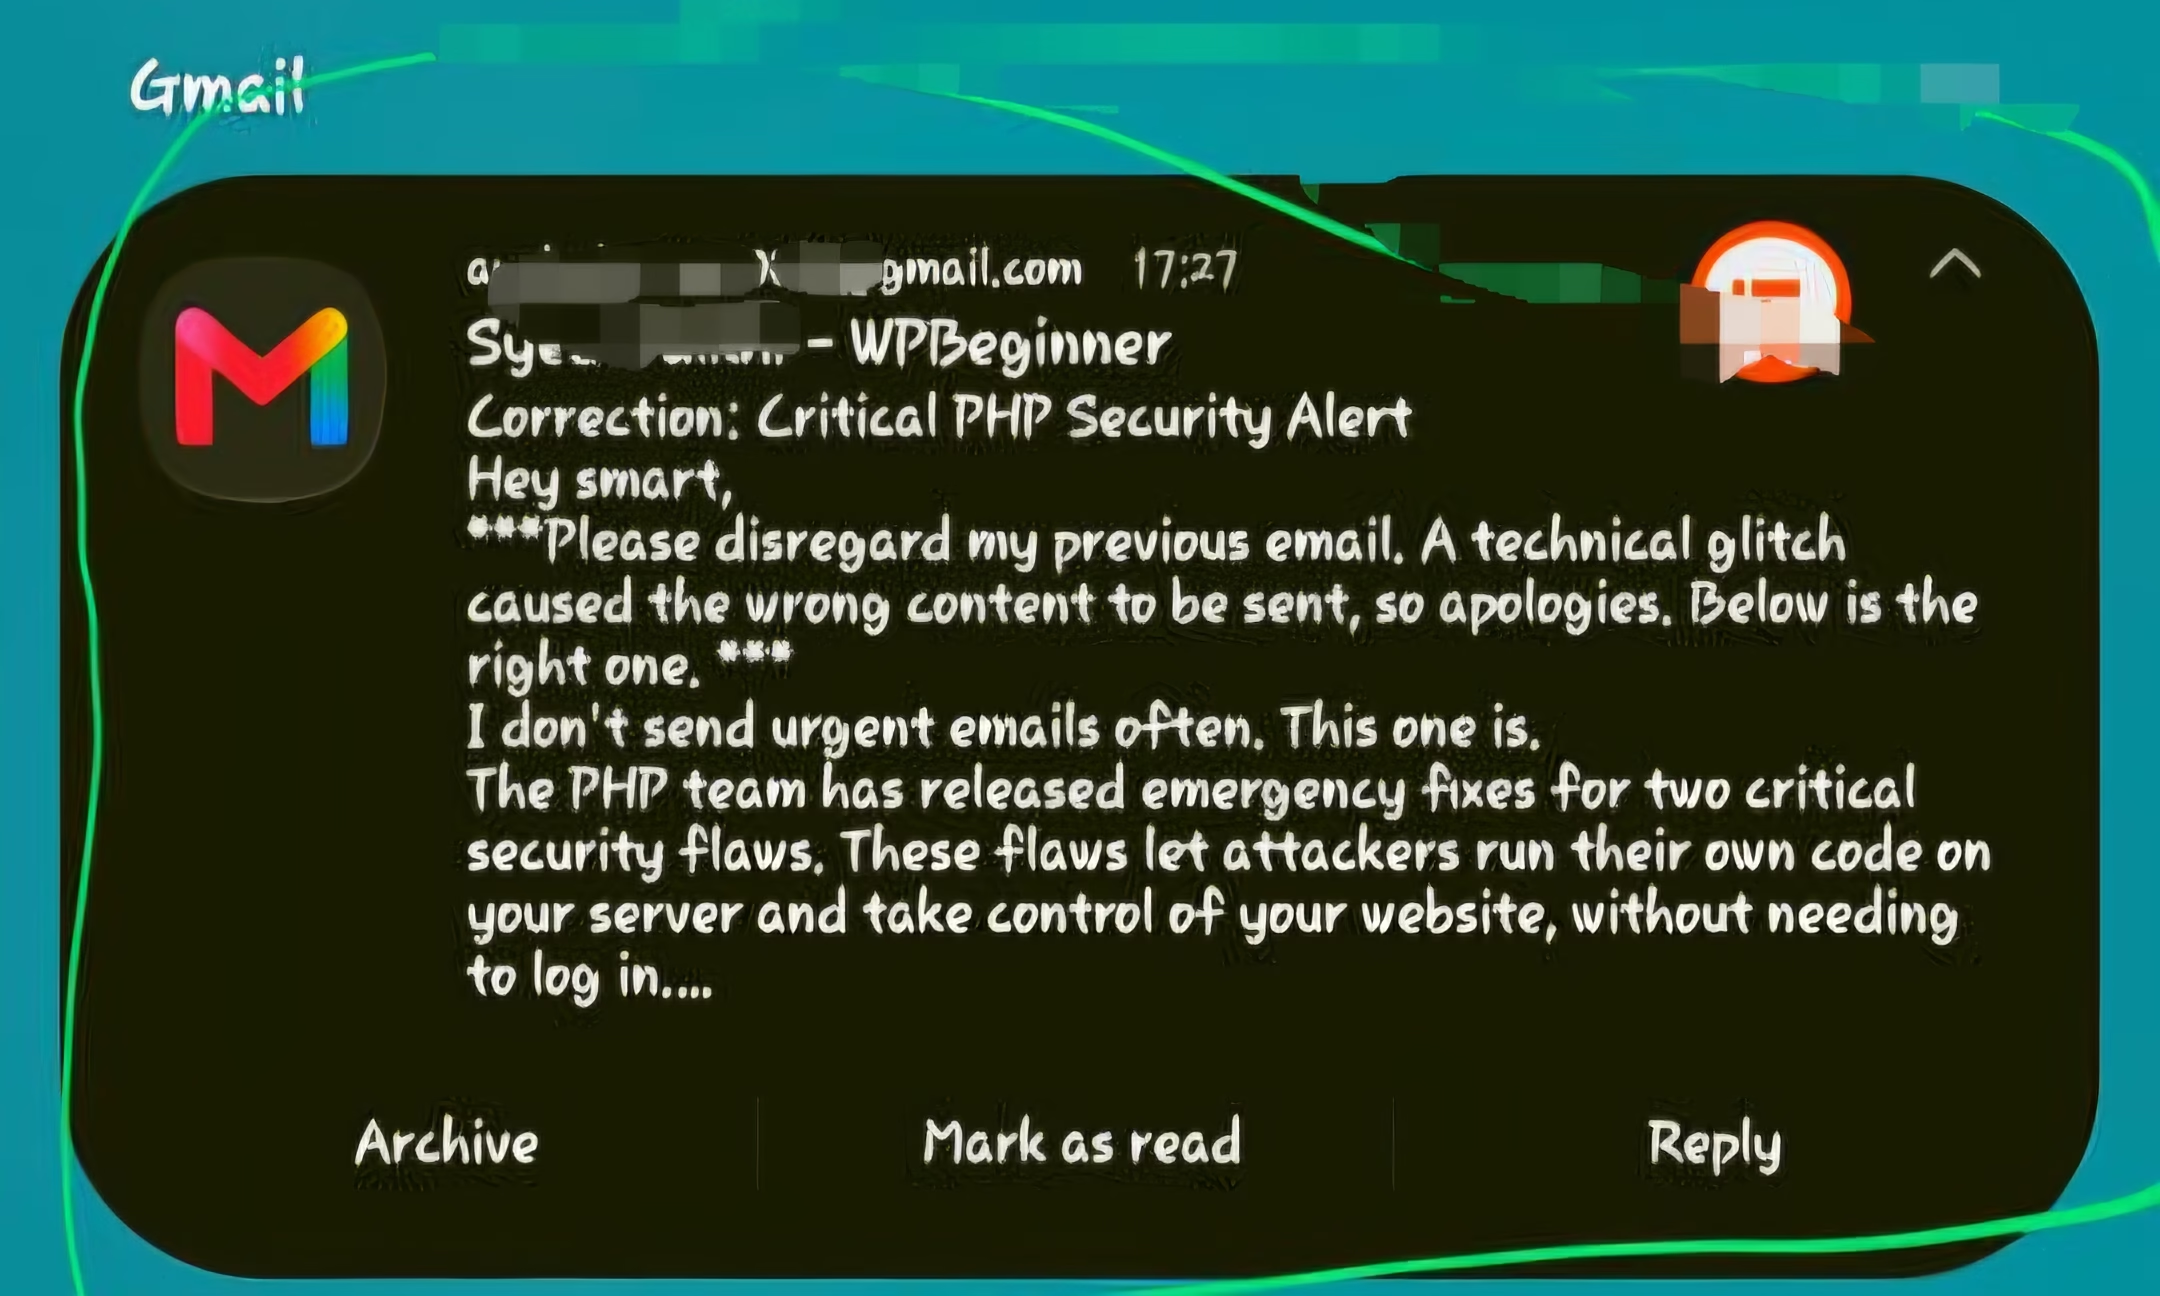
The vulnerabilities carry a severity score of 9.2 out of 10 under the CVSS 4.0 system. Successful exploitation could allow attackers to run commands on affected servers, expose sensitive information or compromise websites and applications.
The incident highlights the security risks associated with widely used software infrastructure and the growing role of artificial intelligence in discovering and exploiting vulnerabilities.
PHP is a server-side programming language used to build and operate websites and web applications. It underpins popular content management systems, including WordPress, Drupal and Joomla, as well as other online services.
According to cybersecurity firm Wiz, the vulnerabilities affect PHP’s core engine rather than a specific website platform or plugin. Consequently, a website could be exposed even if its application code has no known security flaw.
The vulnerabilities involve memory-management errors that can occur when PHP handles abnormal request termination. One concerns corrupted internal state following an out-of-memory condition, while the other involves stale references to memory that has already been released.
Researchers demonstrated that the flaws could be chained to achieve remote code execution, potentially giving an unauthenticated attacker control over processes running with the privileges of the affected PHP service.
Depending on the server’s configuration and permissions, successful exploitation could expose database credentials, authentication tokens and other sensitive information. Attackers could also alter website content, install malicious files or disrupt services.
The PHP security team released fixes on October 21 and urged administrators to update affected installations. The official advisory covers internet-facing PHP deployments, including PHP-FPM, Apache’s mod_php, php-cgi, FrankenPHP and LiteSpeed.
The disclosure quickly escalated into an international security response as organisations assessed their exposure and applied patches.
Reuters reported that Cloudflare observed thousands of attempted exploits in the 10 hours before the vulnerability was publicly announced. The volume rose to tens of thousands within 45 minutes of the announcement and hundreds of thousands within two hours, eventually reaching millions, according to Cloudflare chief executive Matthew Prince.
The surge underscored concerns that attackers could rapidly turn public technical information into working exploits against systems that remained unpatched.
Several governments and businesses temporarily suspended online services as a precaution. Reuters reported disruptions involving government services, financial institutions, airlines, transport operators and other organisations across Europe and Asia.
France’s Orange temporarily suspended access to certain PHP-based websites and applications, while Finland’s state IT services provider Valtori worked through security updates before gradually restoring affected services.
Japanese organisations, including Nomura, Mitsubishi UFJ Financial Group and ANA, also reported temporarily suspending some internet services as part of emergency measures.
However, precautionary shutdowns should not be confused with confirmed compromises. Valtori said its service disruptions were not caused by exploitation of the vulnerabilities and that it was not aware of an active breach involving the flaws.
The response demonstrates the operational challenges involved in securing interconnected systems, particularly where administrators must patch software, test compatibility and verify that critical services remain functional.
The discovery has also drawn attention to how artificial intelligence is changing vulnerability research.
In a report published on October 21, Wiz said its researchers used AI models to help investigate weaknesses in PHP’s core engine and develop working exploits. The company said the underlying issues had remained in the codebase for more than a decade, but exploiting them required complex technical work.
According to Wiz, AI significantly reduced the effort needed to develop and adapt exploit techniques across different applications. The research involved coordination with the PHP team and other cybersecurity contributors before the fixes were released.
The development illustrates the dual-use nature of AI in cybersecurity. Researchers can use advanced models to uncover weaknesses, verify fixes and strengthen software. Attackers may also use similar capabilities to analyse public disclosures and automate parts of the exploitation process.
That possibility has increased pressure on organisations to patch vulnerable systems quickly rather than relying solely on the assumption that complicated vulnerabilities will be difficult to exploit.
The European Union Agency for Cybersecurity, the European Commission, CERT-EU, Europol’s European Cybercrime Centre and national cybersecurity response teams issued a joint warning urging organisations to address the vulnerabilities immediately.
Their guidance recommends identifying PHP-based applications, coordinating with hosting providers and prioritising systems accessible from the internet. Organisations unable to remediate exposed systems immediately should consider isolating them from public networks until fixes can be applied.
The patched releases identified in the PHP security advisory are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. Administrators should use the appropriate fixed release for their branch or a security update supplied by their operating-system or hosting vendor.
Older, unsupported PHP versions require particular attention because they may not receive standard upstream security updates. Organisations using such installations should consult their vendors about available fixes and plan an upgrade to a supported version.
Updating a content management system or its plugins alone may not resolve the problem because the vulnerabilities exist in the underlying PHP runtime. Website operators should confirm that the live server has been patched, review security logs for suspicious activity and investigate possible compromise where necessary.
The immediate priority is to close the vulnerability before attackers can exploit it. For organisations that depend on PHP to publish information, provide services or process sensitive data, the incident is a reminder that maintaining the software beneath a website is as important as securing the application itself.
Sources: PHP security advisory, Reuters, Wiz Research, European Union Agency for Cybersecurity.


Copyright © 2025 - The Bit Gazette.