- Trending
- Comments
- Latest
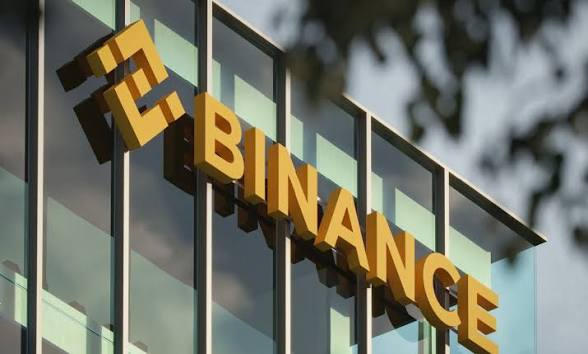
The hacker behind the Binance breach split about 18,270 bitcoin, worth roughly $1.4 billion, across 19 wallets within minutes of the withdrawal, CoinDesk’s analysis of blockchain data shows. Unlike USDT or USDC, bitcoin has no issuer that can freeze it, and as of 04:23 UTC on Friday none of the wallets had sent any funds out.
According to blockchain transaction data examined by CoinDesk, the Binance hacker transferred approximately 18,270 BTC from an exchange-controlled hot wallet on Thursday, October 29, 2026.
The Bitcoin was valued at approximately $1.4 billion based on market prices early Friday, making it one of the largest individual cryptocurrency movements associated with the security incident.
The initial transfers occurred at approximately 20:20 UTC. Eleven transactions moved the Bitcoin from a Binance hot wallet into an address controlled by the attacker. All 11 transactions were confirmed in Bitcoin block 973,732.
Rather than keeping the stolen cryptocurrency in one destination, the Binance hacker quickly divided the funds into multiple wallets. Blockchain tracking showed that the distribution process began almost immediately after the Bitcoin reached the receiving address.
The attacker employed a transaction technique commonly known as a peel chain. This method involves repeatedly transferring portions of cryptocurrency into newly generated addresses while moving the remaining balance through subsequent transactions.
In this particular case, approximately 1,000 BTC was separated into individual addresses during successive transactions. Some remaining balances were temporarily combined before being divided again, creating additional transaction paths.
At 04:23 UTC on Friday, October 30, none of the 19 destination wallets had recorded an outgoing Bitcoin transaction. Although the addresses received small unsolicited deposits from other blockchain users, there was no reported movement of the original stolen Bitcoin at that time.
One of the most significant aspects of this incident is the difference between Bitcoin and stablecoins when it comes to asset recovery.
Unlike Bitcoin, several stablecoins operate through smart contracts controlled by issuing organisations.
Companies behind assets such as USDT, USDC and XRP-related infrastructure have mechanisms that can restrict transactions involving specific addresses under certain circumstances.
This capability has become particularly relevant during the Binance security incident. Blockchain intelligence firm TRM Labs reported that several stablecoin issuers had taken action against addresses associated with the attacker.
Bitcoin operates differently. Its decentralised network does not have a central issuing organisation with the authority to blacklist addresses or reverse transactions simply because they have been associated with a theft.
Consequently, the Binance hacker can hold the Bitcoin in separate wallets without facing the same immediate issuer-level restrictions that apply to certain stablecoins.
However, this does not mean the stolen assets are completely beyond recovery. Investigators can continue monitoring the addresses, identifying transaction patterns and cooperating with cryptocurrency exchanges and other service providers to prevent the funds from entering accessible trading platforms.
The investigation has also raised questions about the identity of the organisation responsible for the attack.
TRM Labs, a blockchain intelligence company, attributed the theft to TraderTraitor, a sophisticated North Korean hacking unit. The company described its assessment as being made with “high confidence,” based on its investigation and intelligence.
The group has previously been associated with major cryptocurrency thefts, including the February 2025 Bybit incident, in which approximately $1.5 billion worth of digital assets was stolen.
According to TRM Labs, the group previously spent around 10 days converting assets stolen during the Bybit incident from Ethereum into Bitcoin.
The Binance hacker’s decision to distribute the stolen Bitcoin across multiple wallets has therefore attracted particular attention from blockchain investigators, especially given the group’s previous involvement in large-scale cryptocurrency thefts.
Binance’s preliminary investigation also provided some insight into how the latest incident may have occurred.
In an official security update published on October 30, the exchange said a compromised laptop belonging to a DevOps engineer may have allowed the attacker to access a service container and submit unauthorised withdrawal transactions.
The exchange also confirmed that it was working with law enforcement agencies and blockchain intelligence partners to trace the stolen assets and support recovery efforts.
The incident carries important implications for cryptocurrency investors, particularly those who hold assets on centralised exchanges.
Although Binance remains one of the world’s largest cryptocurrency trading platforms, the breach highlights the operational risks associated with keeping substantial digital asset reserves in internet-connected wallets.
Hot wallets are designed to facilitate withdrawals and other transactions quickly. However, their constant connection to online systems can expose them to security threats if internal access controls, employee devices or transaction approval processes are compromised.
Beyond the Bitcoin theft, the wider security incident reportedly affected approximately $6.3 billion in digital assets across multiple blockchain networks.
Binance said it had worked with blockchain partners to freeze approximately $3 billion in affected assets and would cover the losses using its Secure Asset Fund for Users (SAFU) and company funds.
The exchange also temporarily suspended deposits and withdrawals while security checks were conducted.
At the time covered by the original CoinDesk investigation, the 18,270 BTC remained distributed across the 19 wallets without any recorded outgoing transactions.
Whether the attacker eventually attempts to move the funds through exchanges, trading desks or other conversion services remains an important question for investigators and market participants.
The movement of approximately $1.4 billion in Bitcoin across 19 wallets represents a significant development in the wider Binance security breach.
Although blockchain transparency gives investigators the ability to monitor the stolen assets, Bitcoin’s decentralised architecture limits the possibility of freezing them through a central authority.
The Binance hacker’s next moves could determine whether investigators have an opportunity to recover more of the stolen cryptocurrency or whether the funds remain inaccessible for an extended period.
Crypto investors will therefore be watching developments closely as Binance continues its investigation and works with industry partners to strengthen security.

Copyright © 2025 - The Bit Gazette.