- Trending
- Comments
- Latest
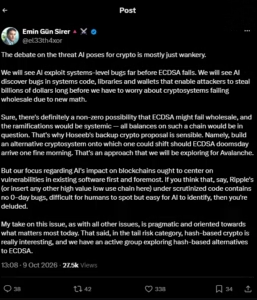
Avalanche founder Emin Gün Sirer says the bigger danger to crypto is not AI breaking cryptography but AI finding the software bugs developers missed. His October 9 post challenges Ethereum Foundation researcher Justin Drake’s call for “bunker mode,” a plan to move funds to fresh addresses in case signatures weaken.
In a post on X on October 9, Sirer challenged what he viewed as an exaggerated focus on the possibility that AI could break cryptographic protections.
“The debate on the threat AI poses to crypto is largely just talk,” he wrote.
Sirer’s argument centers on the difference between developing a capability that can defeat established cryptographic algorithms and using AI to discover mistakes in existing code.
Cryptocurrency networks depend on complex software to manage transactions, authenticate users, interact with wallets and enforce protocol rules. Even when the underlying cryptography remains secure, weaknesses in the code implementing those functions can create opportunities for attackers.
AI-assisted code analysis could make it easier to identify programming errors, unexpected interactions and vulnerabilities that conventional testing has missed. If attackers discover and exploit those weaknesses before developers release fixes, they could potentially gain unauthorized access to funds or compromise other parts of a blockchain ecosystem.
Sirer pointed to Ripple and other networks holding substantial value as examples of systems whose code may contain weaknesses that have escaped sufficiently thorough review. The supplied report does not identify a specific vulnerability in Ripple or establish that its network has been compromised.
The broader concern is that software complexity makes it difficult for developers to guarantee that every possible weakness has been identified. AI could accelerate the discovery process, potentially giving both security researchers and malicious actors new ways to examine large codebases.
However, AI detection does not automatically translate into successful exploitation. A vulnerability’s severity depends on its location, the conditions required to exploit it and the effectiveness of existing security controls.
The debate intensified on October 7 after Ethereum Foundation researcher Justin Drake called on the industry to prepare for what he described as a potential emergency security scenario.
Drake recommended a precautionary approach he called “bunker mode,” which would involve moving funds to previously unused addresses to reduce exposure associated with publicly visible cryptographic keys.
His concerns focus on the Elliptic Curve Digital Signature Algorithm (ECDSA), a digital signature mechanism used by many cryptocurrency wallets and blockchain systems. ECDSA helps users prove control over private keys and authorize transactions without revealing those keys directly.
The security concern is that sufficiently advanced mathematical techniques or computing capabilities could eventually make it easier to derive private keys from exposed public keys. If that became practical, attackers could potentially compromise wallets whose security depends on the affected cryptographic assumptions.
Drake’s scenario suggests that advances driven by AI could accelerate this risk, potentially shortening the time available for networks and users to prepare.
The proposal has received mixed reactions from industry figures. Coinbase’s Yehuda Lindell criticized the perspective, while Ledger’s technical leadership highlighted the risks of rushing a migration to new security arrangements. Ethereum co-founder Vitalik Buterin acknowledged that the issue presents a serious risk but did not call for immediate emergency action, according to the supplied report.
The disagreement reflects the difficulty of balancing precaution against the operational risks of large-scale security changes.
Moving funds to new addresses can reduce certain forms of exposure, but migrations must be carefully designed and executed. Poorly coordinated changes could introduce new vulnerabilities, confuse users or create opportunities for phishing attacks.
The debate also reinforces why crypto software bugs and cryptographic weaknesses require different responses. Replacing or upgrading a signature system may help address future cryptographic risks, but it does not automatically repair vulnerabilities in wallets, applications or the software connecting those systems.
Sirer’s concerns come against a backdrop of continuing cryptocurrency security incidents. The supplied report states that the crypto sector lost approximately $766 million in September, although it does not provide a breakdown of the incidents or establish how much of that amount was attributable to software vulnerabilities.
It also cites a security team demonstration from the summer that reportedly showed AI identifying 85 critical vulnerabilities. The original material does not identify the team, the systems examined or the methodology used, so the figure cannot independently establish the scale of the threat across the industry.
Nevertheless, these examples illustrate why developers are paying increasing attention to AI-assisted security testing.
Traditional security reviews rely on code audits, testing, threat modelling and monitoring. AI tools could supplement those processes by examining large volumes of code, identifying suspicious patterns and suggesting ways a vulnerability might be triggered.
The technology could also help security teams prioritize remediation by highlighting flaws that appear particularly consequential. But results still require validation, and the quality of AI-generated findings depends on the tools, available context and systems being examined.
His position is that improving existing software should come first, rather than allowing concerns about a possible future cryptographic breakthrough to overshadow current weaknesses.
The issue extends beyond individual networks. The report estimates that more than six million bitcoins rely on already visible public keys, representing over 31% of the circulating supply. Drake’s proposed migration is intended to reduce this exposure, although the report does not provide an independent breakdown of the estimate or the assumptions behind it.
Visible public keys do not automatically mean that the associated bitcoin holdings are vulnerable to an immediate attack. The practical risk depends on the cryptographic system involved and whether an attacker has the capability to derive the corresponding private keys.
The emerging debate does not present software vulnerabilities and cryptographic threats as mutually exclusive problems. Instead, it highlights the need for cryptocurrency networks to prepare for both.
In the near term, identifying and repairing crypto software bugs could help reduce risks that already exist in wallets, smart contracts, applications and supporting infrastructure. AI-assisted auditing may strengthen those efforts, provided developers verify findings and implement appropriate fixes.
Over a longer horizon, networks may also need to prepare for advances that could weaken cryptographic assumptions underpinning digital signatures and account security.
That preparation could involve researching alternative cryptographic techniques, planning carefully controlled migrations and developing clear procedures for protecting users if existing systems become unsafe.
Sirer’s warning ultimately challenges the industry to balance long-term preparation with immediate security work. While a breakthrough capable of undermining cryptographic signatures could have far-reaching consequences, overlooked software flaws can create opportunities for attackers even when the underlying mathematics remains intact.
As AI tools become more capable, the central question for blockchain developers will be whether they can use those tools to discover and eliminate weaknesses faster than attackers can exploit them.

Copyright © 2025 - The Bit Gazette.